
Badware Forwarding
I'm not entirely sure on who is doing the actual badware checking, i suspect it might be either Theia or R5AC.
While apex had still used EAC+Theia, there used to be a callback that inside the game that was called everytime a badware detection has fired. So the flow is you get the badware message, and in the background, Apex might send the violation possibly containing an identifier for the blacklisted tool that was detected.
I did a quick test by first neutralizing R5AC::PushViolation, and then monitoring it while simultaneously launching IDA Pro, which apparently was on their list of applications considered as badware. The result was that PushViolation was called multiple times nearly imemdiately after the blacklisted application was launched.
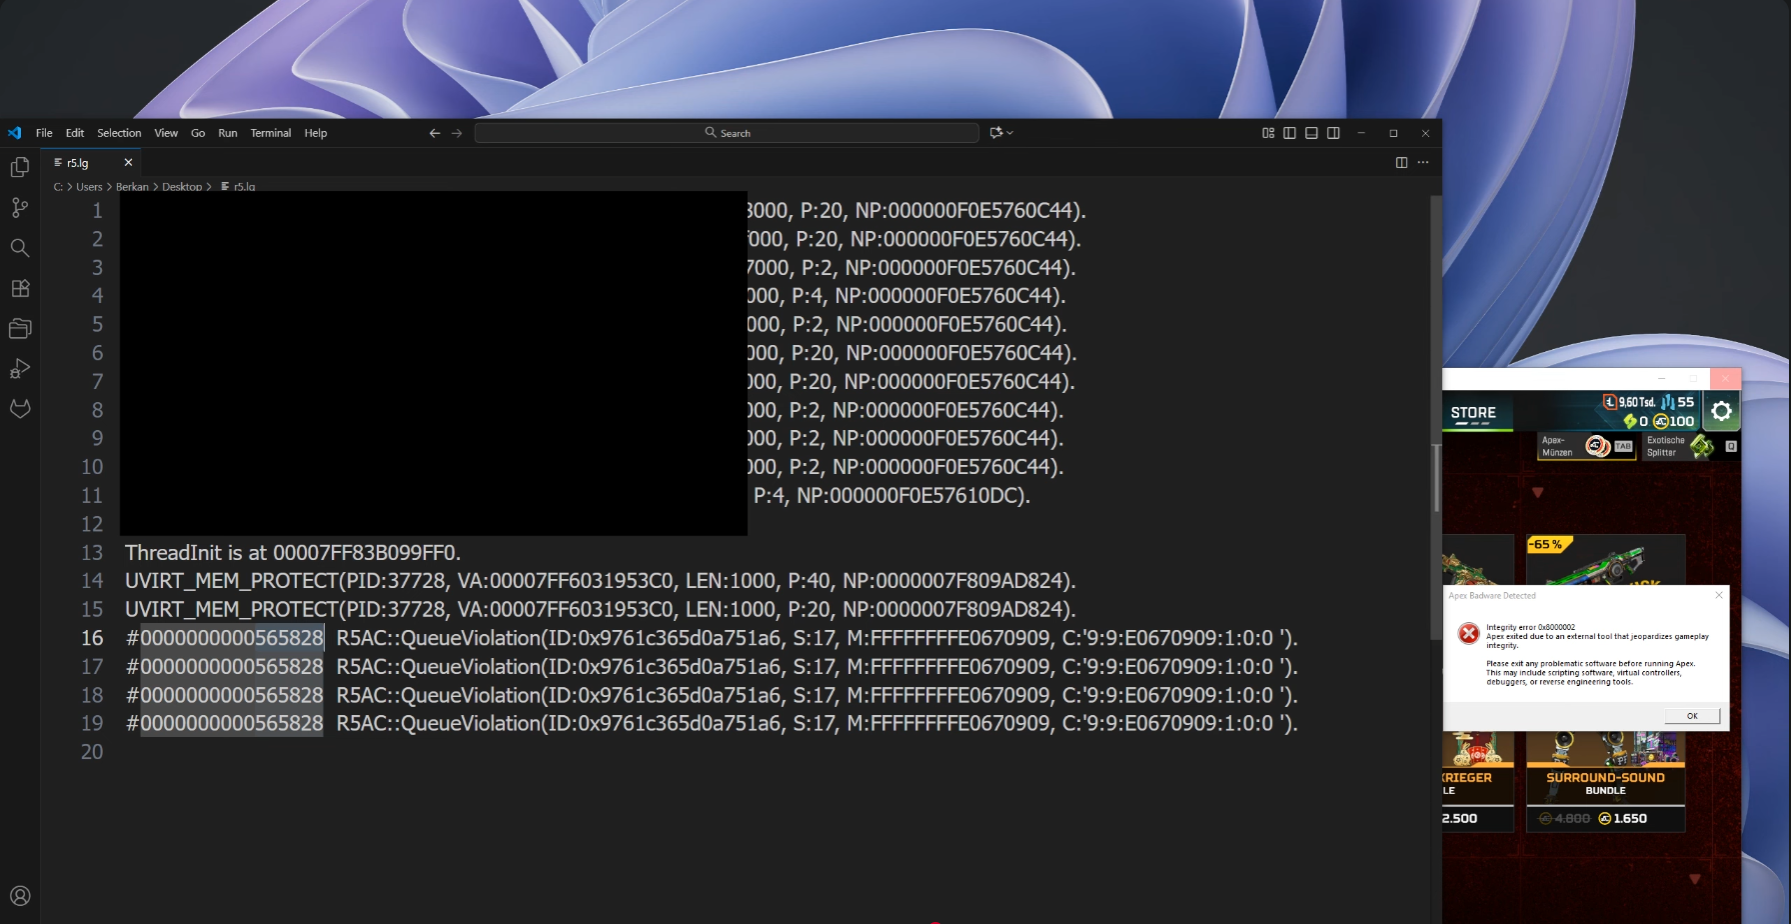
I should have tried launching cheat engine or some other blacklisted program and compare the c-string it passed to PushViolation. Sadly i have not done that so i can only speculate if they actually have a way of distinguishing the blacklisted application that was detected. It would certainly make sense though, purely from a detection perspective.
https://www.youtube.com/watch?v=Tcc6eExS7hk
It should be noted that this is one of the few functions that make use of the R5AC::PushViolation variant that, under the conditions where the game client currently has an active network channel to the game server, it will attempt to transmit the violation message directly via C_NetChan::SendNetMsg and C_NetChan::SendDatagram.
No comments to display
No comments to display